Fake Video Call Scam: The "Fix Your Audio" Trap
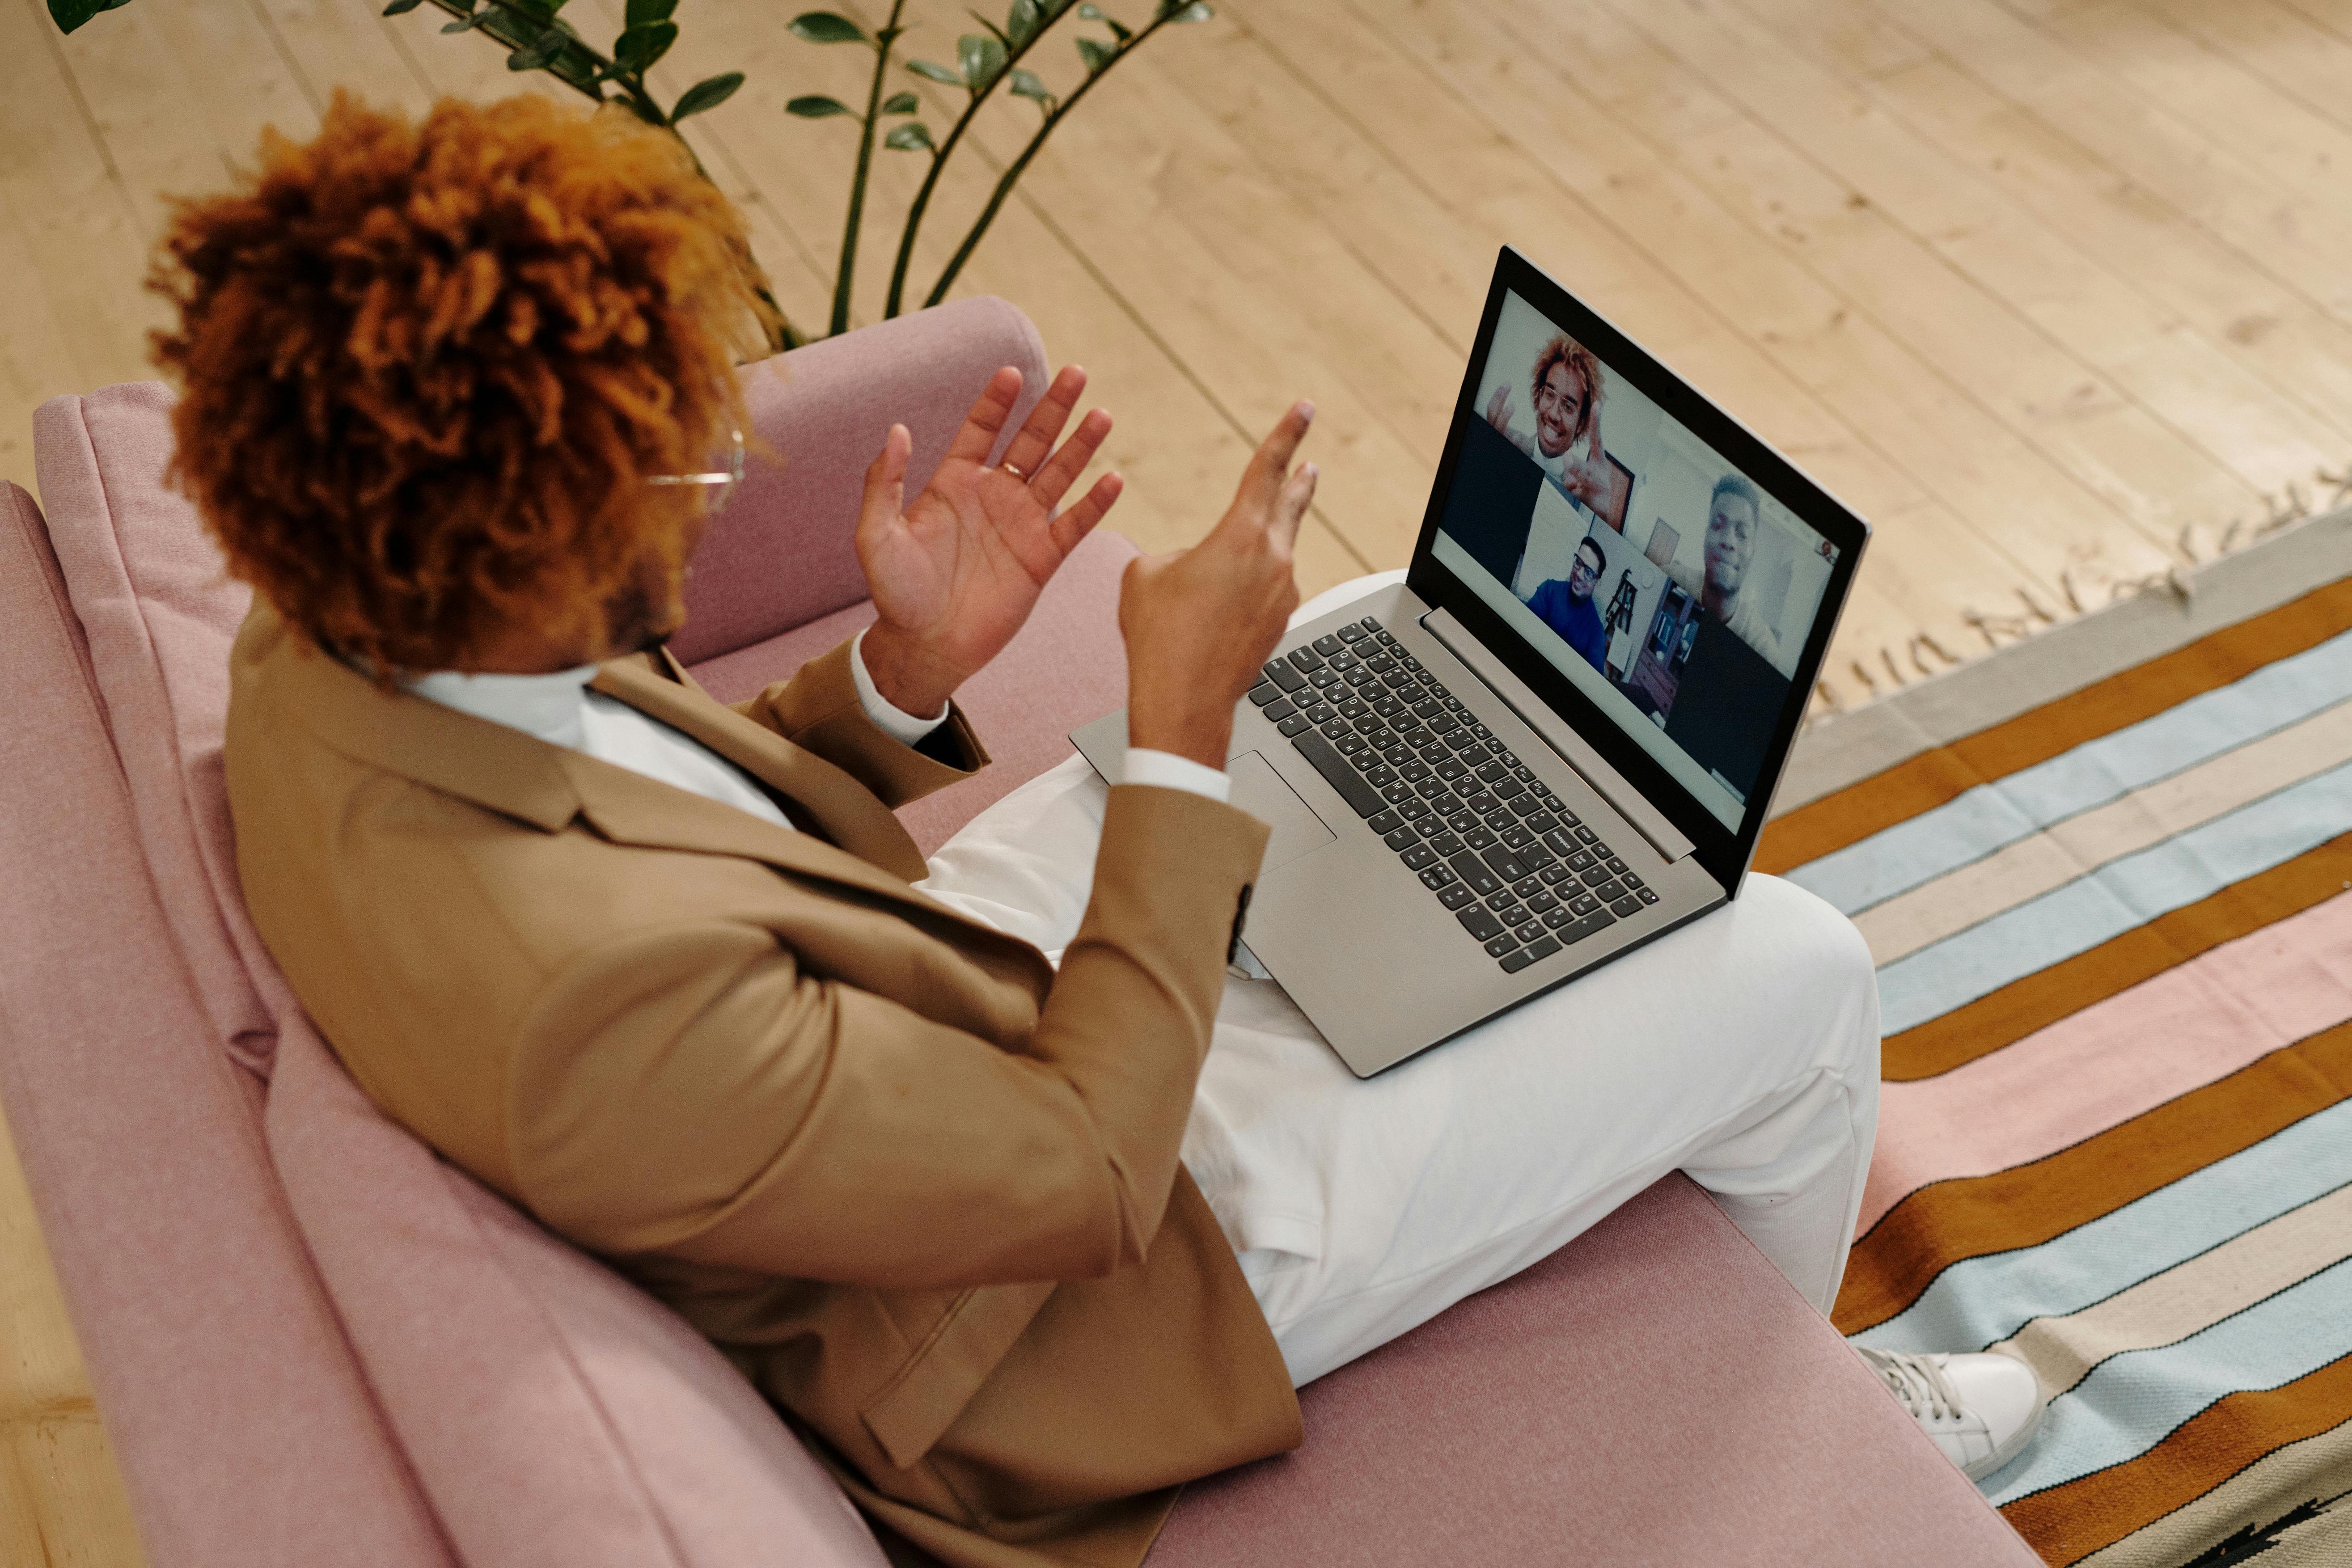
You get a message from a colleague or contact you know. They want a quick video call. You click the link, see their face in the waiting room, and then they say, "I can't hear you, run this update." That is a fake video call scam, and on November 12, 2026 the FBI published a detailed warning about it.
The FBI calls this version "FaceStealer." Its warning is aimed at people in cryptocurrency and open-source software, but the trick works on anyone who takes video calls. The details below are about the United States (FBI), so check your own country's official channels if you live elsewhere.
What is the fake video call scam?
In a fake video call scam, criminals send you a link to a copycat of Zoom, Microsoft Teams or Google Meet. According to the FBI's FLASH report, North Korean Hackers Use Secretly Recorded Webcam Library of 900+ Tech Workers in $400M "FaceStealer" Crypto Theft Scheme, the FBI attributes the scheme to North Korean state-sponsored hackers. The FBI says it has stolen more than $400 million in cryptocurrency over 18 months.
What makes it hard to spot is that the person on screen looks real. The FBI says the hackers play prerecorded webcam video of earlier victims, so you see someone you know "joining" the call. The FBI has seized more than 900 such videos. It also warns that AI-generated deepfakes are starting to appear, though real stolen video is still the main tool.
How the fake video call scam works, step by step
The FBI's FaceStealer overview describes a repeating cycle:
A real account is hijacked. Hackers take over a victim's Telegram, LinkedIn, Slack or Discord account and secretly record their webcam.
Their contacts get a message. It looks like it comes from a friend or colleague and suggests a catch-up, a collaboration or an investment chat. Hackers can read old chats, so the message can feel personal.
A meeting link arrives, often late. The FBI says the link is a lookalike domain, not the real Zoom or Teams. It may be sent only shortly before the meeting, often after a calendar invite that had no video link in it.
The call looks normal. You see the recorded video of the person who invited you, sometimes alongside other "participants."
A fake problem appears. You are told that nobody can hear you and are walked through a "fix": an update button, a script, or code to paste into a terminal. That fix installs malware.
NBC Los Angeles, reporting on the FBI Los Angeles office's warning, quotes FBI Special Agent Jeremy Robertson: "You're looking at a video of a prior victim." The FBI says the victims it saw were experienced crypto and Web3 executives, developers and even cybersecurity experts, which shows that being tech-savvy does not make you immune.
Why the fake video call scam fools smart people
It does not rely on a strange email or bad spelling. It borrows trust you already have: a real account, a real face and a real chat history. A "problem" in front of several people creates social pressure to fix it fast, and the fix looks like routine maintenance.
The FBI also notes that stolen access is not always used right away. In several cases hackers waited months or more than a year, watching crypto balances grow before taking the money.
How to protect yourself from a fake video call scam
These tips come from the recommendations in the FBI FLASH report:
- Join with the official app, not a link. Open Zoom or Teams yourself and use the meeting ID or invite code, especially for new or infrequent contacts.
- Keep your webcam off until you can see and talk to the person. This gives you a chance to check them before handing over your video.
- Never run scripts or paste code to "fix" a call. If a meeting asks for an update, close it and update the app separately.
- Read calendar invites closely. An invite with no meeting link, followed by a link at the last minute, is a warning sign.
- Confirm by another channel. If the invite came by Telegram, check by text or phone that your contact really sent it.
- Lock down your chat apps. Turn on multifactor authentication and login alerts, and consider expiring messages so less chat history is exposed if an account is hijacked.
- Keep crypto away from your daily device. The FBI says to keep only small amounts in browser extension wallets and never store recovery phrases on a device.
What to do if you think you were caught
The FBI's guidance if you suspect a compromise:
- Move any crypto to a new wallet with new recovery phrases, set up on a different, clean device.
- Change passwords, sign out of all active sessions and add multifactor authentication on messaging and developer accounts.
- Tell your contacts and, if work files were on the device, your employer. Staying quiet helps the scheme spread.
- Report it at IC3.gov using the keyword "FaceStealer" (US).
For general advice on any scam you may have fallen for, the FTC's guide "What To Do If You Were Scammed" is a good next step in the United States.
My take
I have not had this happen to me — nobody has ever asked me to run a fix or install something in the middle of a video call. Reading the FBI's warning, though, I can see how easily it would work: if a familiar face is on screen and everyone seems to be waiting on you, the pressure to just click the update is real. My rule from now on is simple — if a call ever asks me to run a script, paste code, or install anything, the call ends there, and I will open the app myself and check with the person on a separate call or message. That is also what I am telling my family: a face on the screen is not proof anymore, and no genuine meeting needs you to install something just to be heard.
The bottom line
A familiar face on a video call is no longer proof of who is there. Before you click, check the invite another way, join through the official app, keep your camera off at first, and never run a "fix" someone types into the chat.
Your turn
Have you ever been asked to install an "update" in the middle of a video call? How did you decide whether to trust it? Share your tip in the comments.
Sources
- FBI, FaceStealer Cryptocurrency Theft Scheme
- FBI FLASH AC-111226-MS, North Korean Hackers Use Secretly Recorded Webcam Library of 900+ Tech Workers in $400M "FaceStealer" Crypto Theft Scheme (12 November 2026)
- NBC Los Angeles, FBI's LA Field Office warns of 'FaceStealer' cryptocurrency theft scheme (12 November 2026)
- FTC, What To Do If You Were Scammed


Comments
Post a Comment